
ModSecurity and increasingly high CPU usage by httpd Apache process
We've run over a massive server slowdown over the first weeks of a migration from CEntOS 7 to AlmaLinux 8. Here is the overview of the situation.
Update of November 12, 2026
On AlmaLinux 8.10, the effects of this additional load on the server are particularly noticeable during a DDoS attack.
Issue
On a Plesk 18 server with multiple websites running, httpd processes are using a lot of CPUs and requests are sometimes slow. The situation is getting worse over time. Plesk is running with normal settings (no major custom settings) and has ModSecurity 2.9 on Apache with Comodo ruleset.
What is really going on
Request are using a lot of CPUs because of ModSecurity ruleset. Disabling ModSecurity temporarily proves it.
The file at /var/lib/mod_security/apache-ip.pag is growing fast, and is slowing down the requests the more it grows.

Solutions
Solution 1 : use another ruleset
Switching to ModSecurity 3.0 on nginx with OWASP ruleset fixed the issue. But it is a completly different ruleset.
In that case, it might be a good idea to make sure that requests are going through nginx as much as possible, by making sure all website use FPM application served by nginx. But all requests seems to go through nginx anyway, so I am not sure this is required.
The following SQL query to psa database can give a quick list of all websites not using this PHP handler:
SELECT d.name, wsp.value FROM domains AS d
LEFT JOIN dom_param as dp ON dp.dom_id = d.id AND param = "webServerSettingsId"
LEFT JOIN WebServerSettingsParameters as wsp ON wsp.webServerSettingsId = dp.val AND wsp.name = "nginxServePhp"
WHERE wsp.value = "false"
Solution 2 : empty the file
An empty or lightweight apache-ip.pag file should also solve the issue. For exemple, running this command daily would keep the database manageable:
systemctl stop httpd
rm -f /var/lib/mod_security/apache-ip.pag /var/lib/mod_security/apache-ip.dir
systemctl start httpd
However, emptying this file means losing temporary data and could also weaken security, as this data could be used by ModSecurity rules that rely on the repetition of an action, for example:
- Number of requests from an IP address
- Number of connection attempts from an IP address
The counters are reset when the file is emptied.
Solution 3 : manage apache-ip.pag correctly
Properly managing apache-ip.pag with ModSecurity 2 seems to rely on using modsec-sdbm-util. This utility is included with CPanel (but not with Plesk).
One solution would be to use this utility to keep only the non-expired entries. To achieve this, one could run this script regularly (untested):
modsec-sdbm-util -n /var/lib/mod_security/apache-ip.pag
systemctl stop httpd
rm /var/lib/mod_security/apache-ip.pag /var/lib/mod_security/apache-ip.dir
mv /tmp/new_db.pag /var/lib/mod_security/apache-ip.pag
mv /tmp/new_db.dir /var/lib/mod_security/apache-ip.dir
systemctl start httpd
Solution 4 : our team's current solution
We are trying to reduce our use of unofficial utilities, especially when they appear to be unmaintained. Therefore, we prefer this approach, which empties the file when it reaches a potentially problematic size.
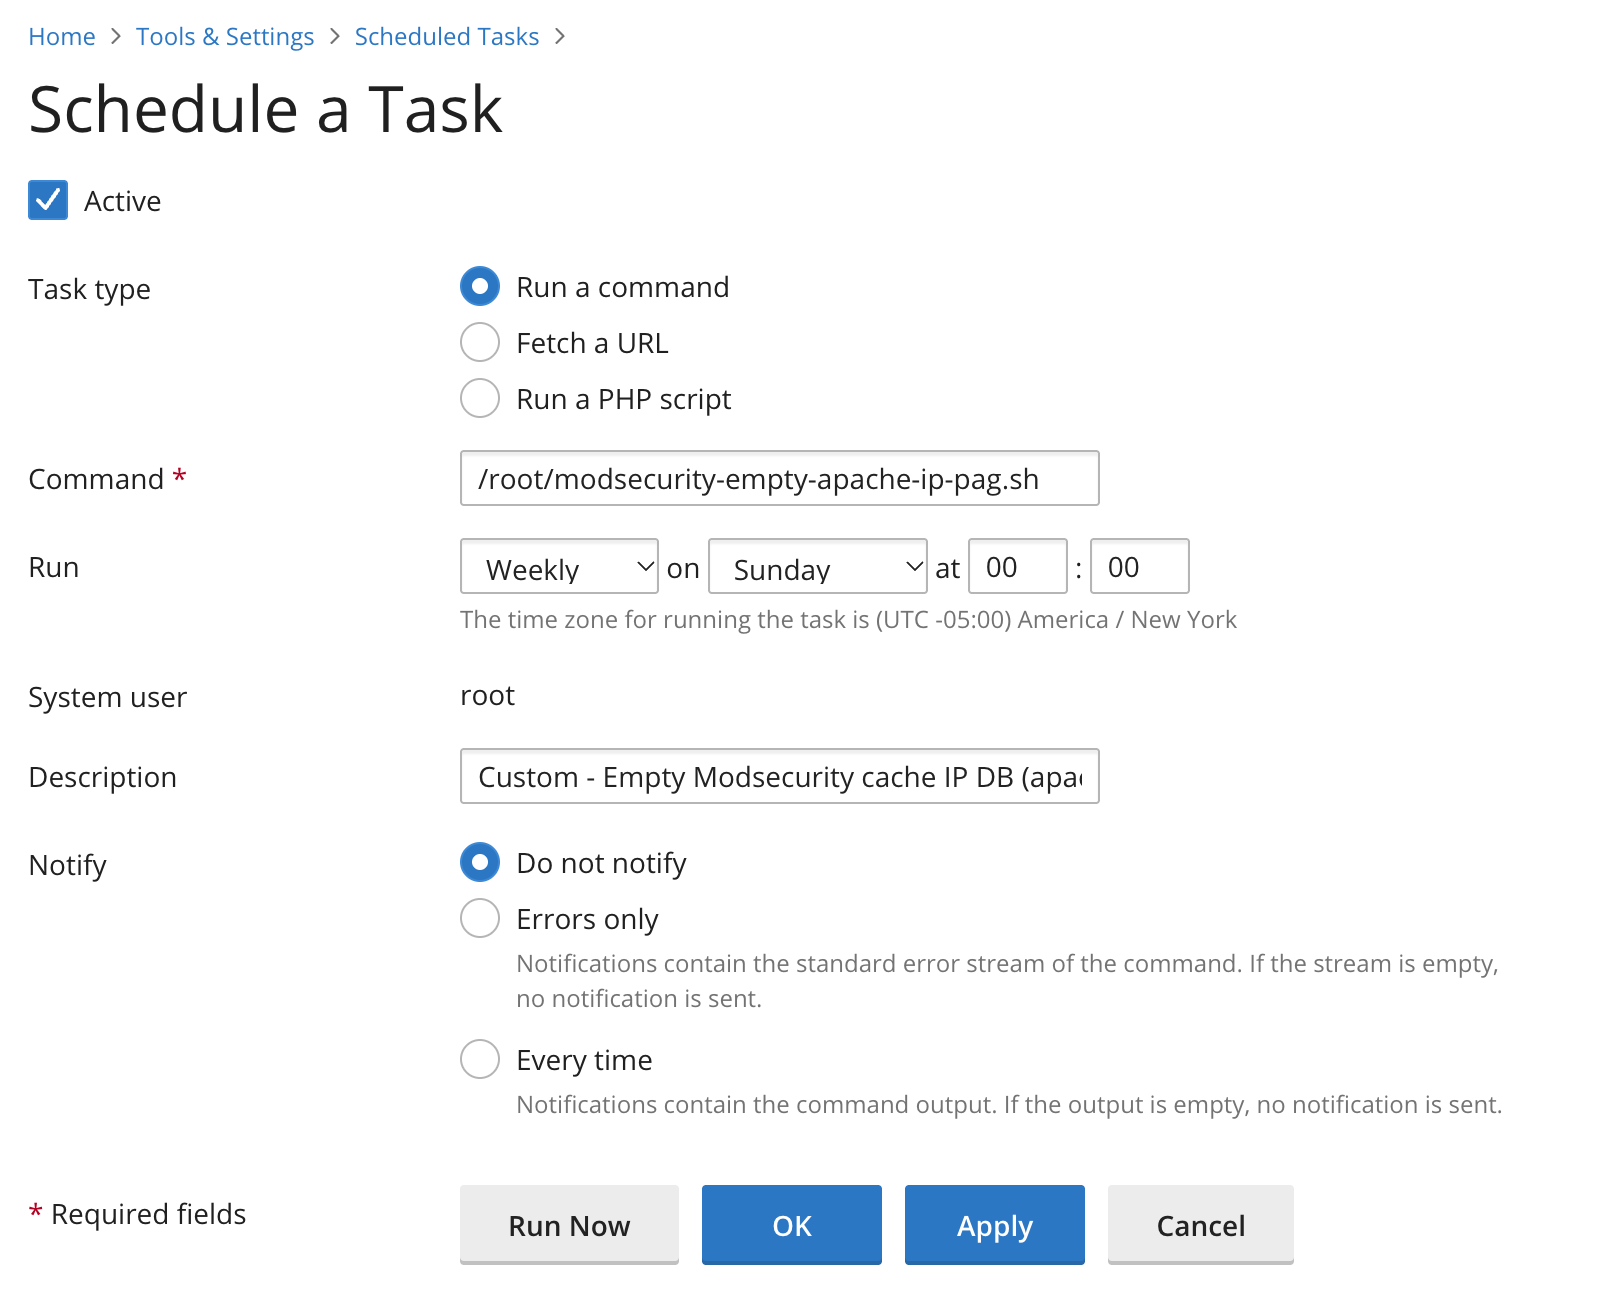
We create the file /root/modsecurity-empty-apache-ip-pag.sh (with execute permissions):
#!/bin/bash

FILE=/var/lib/mod_security/apache-ip.pag # File to check size
LIMIT=$((512 * 1024 * 1024)) # 512 MB in bytes

# Only purge the file when filesize is greater than limit
if [ -f "$FILE" ] && [ "$(stat -c %s "$FILE")" -gt "$LIMIT" ]; then
    systemctl stop httpd
    rm -f /var/lib/mod_security/apache-ip.pag /var/lib/mod_security/apache-ip.dir
    systemctl start httpd
fi
Then we trigger the script regularly using a cron job: